Key points
- Bitcoin Core merged its faster disclosure path on October 22, 2026.
- Easily rediscovered flaws will get fixes for maintained versions and a security advisory promptly.
- The policy change alone does not identify a new emergency upgrade.
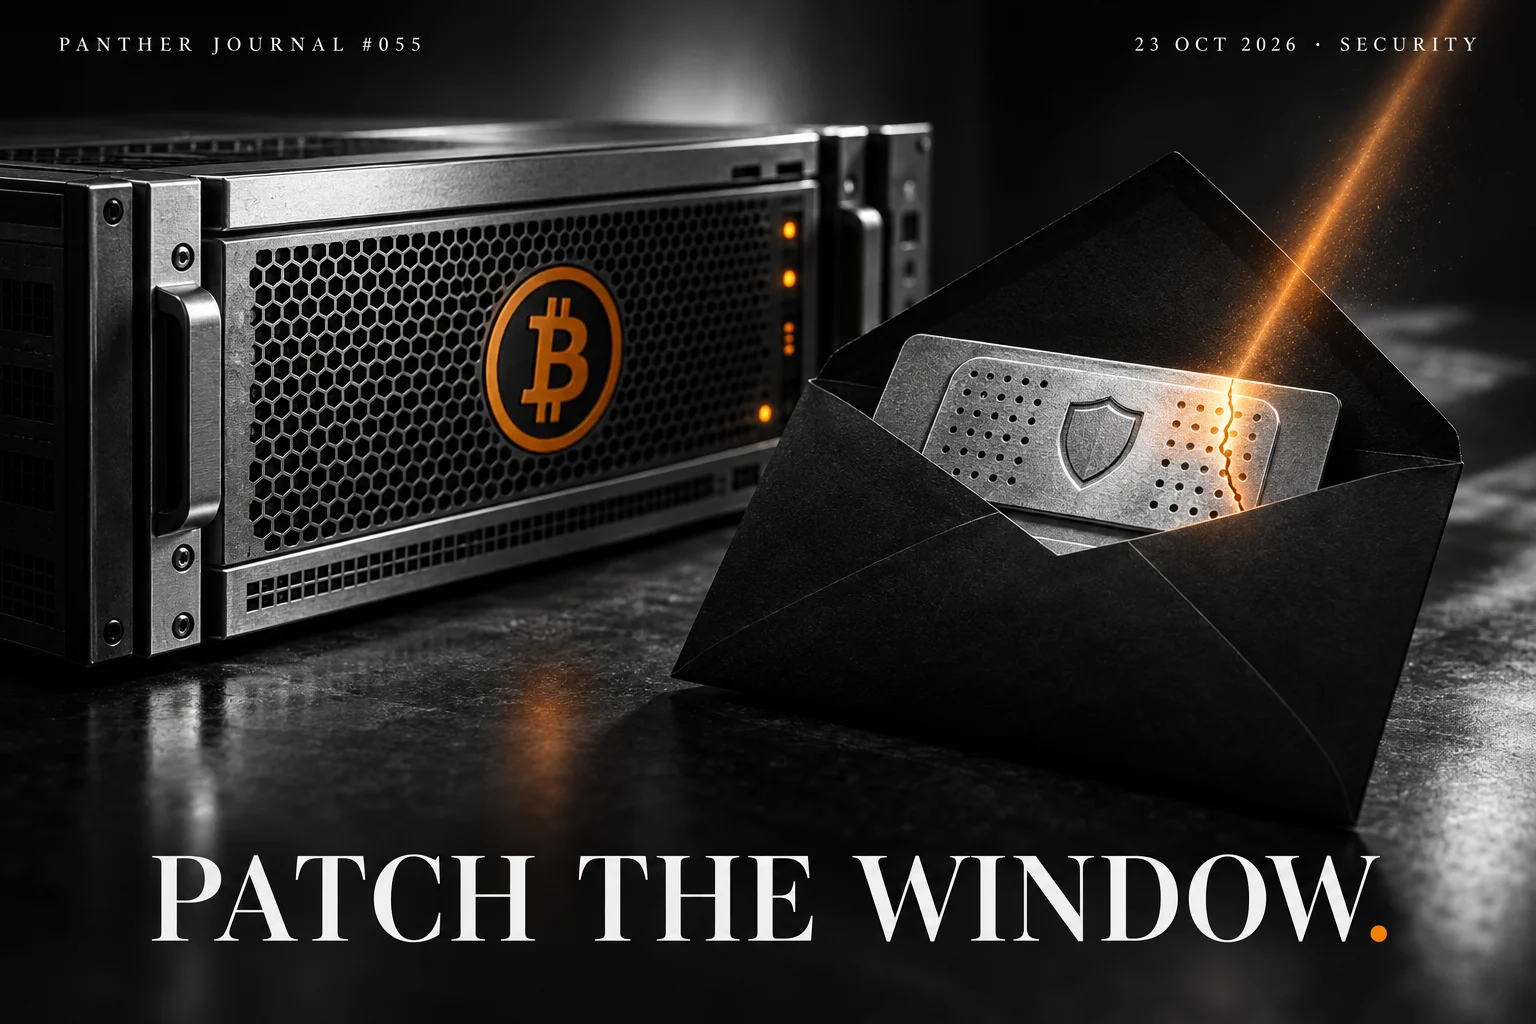
PANTHER JOURNAL #055
A developer ships a quiet fix. An attacker asks a model what changed. The secret may already be gone.
Bitcoin Core has changed its security disclosure policy to address that problem. For vulnerabilities judged easy to rediscover, maintainers will issue fixes for maintained versions and publish an advisory as soon as possible. For Bitcoin ($BTC) node operators, the practical lesson is to watch point releases as closely as major upgrades.
What changed in Bitcoin Core’s security policy?
Pull request #1281 was merged on October 22, 2026. The live policy now gives easily discoverable flaws a faster release path, bypassing the usual severity-based embargo timetable.
That classification can include a flaw found through a simple prompt to a large language model. Maintainers decide during triage; the category extends beyond AI discoveries.
For qualifying issues, each maintained major version should receive a point release containing the fix, accompanied by a security advisory. This is a disclosure procedure, not an announcement that Bitcoin’s keys or cryptography have been broken.
Why can a quiet patch become a warning to attackers?
In the proposal, developer Antoine Poinsot argues that AI has lowered the effort needed to find some bugs or recognise fixes disguised as ordinary code changes. Delaying a release offers less protection when others can cheaply rediscover the problem.
CoinDesk’s October 23 report independently confirms the change and reports that no vulnerability had yet been flagged under the new rule at publication.
The tradeoff remains real. Poinsot’s discussion acknowledges that accelerated fixes may spend less time being tested in development branches. Faster availability helps defenders, while shorter testing creates its own operational challenge.
What should node operators do?
The policy change itself does not identify a new affected version or prescribe an emergency upgrade. Operators should use the relevant advisory when one appears to determine exposure and urgency.
Keep an inventory of deployed versions, follow Bitcoin Core’s official advisories and plan how to test and deploy point releases. An exchange, wallet service or business running nodes needs a named owner for that work.
Panther’s earlier Hoodi configuration report illustrates the same operational principle: a changed announcement only helps when someone checks the running system.
Panther Takeaway
AI is changing the useful lifetime of a software secret. Bitcoin Core is adjusting its release process accordingly.
For operators, the advantage comes from a shorter path between reading an advisory and deploying its fix. Make that path ready before the next notice arrives.
Sources and verification
Primary evidence: the merged Bitcoin Core pull request and current disclosure policy linked above. Independent confirmation: CoinDesk, October 23, 2026. Operator guidance and the implications for response time are Panther’s analysis. No active exploit or new emergency patch is asserted here.
Responses
No responses yet. Start the conversation.
Panther Journal — The intelligence brief
Stay ahead of the story.
Free. New investigations delivered when published. Unsubscribe anytime.