Key points
- Teku 26.10.3 and Besu 26.10.2 remove the affected eMudhra roots from their Docker images.
- Archive and binary installs still depend on the separately managed Java runtime and trust store.
- Default Teku mainnet nodes without HTTPS endpoints were not affected; no exploitation has been reported.
- Operators using remote HTTPS services should verify the running client version, Java build and endpoint protections.
A validator can look healthy while trusting the wrong authority. The Teku eMudhra update turns that lesson into a practical check for Ethereum operators. The Ethereum network itself was not breached, and no exploitation has been reported. But an operator running the wrong combination of client package, Java runtime and remote HTTPS endpoint could have accepted a forged certificate as genuine.
The fix depends on how the software was installed.
What does the Teku eMudhra update fix?
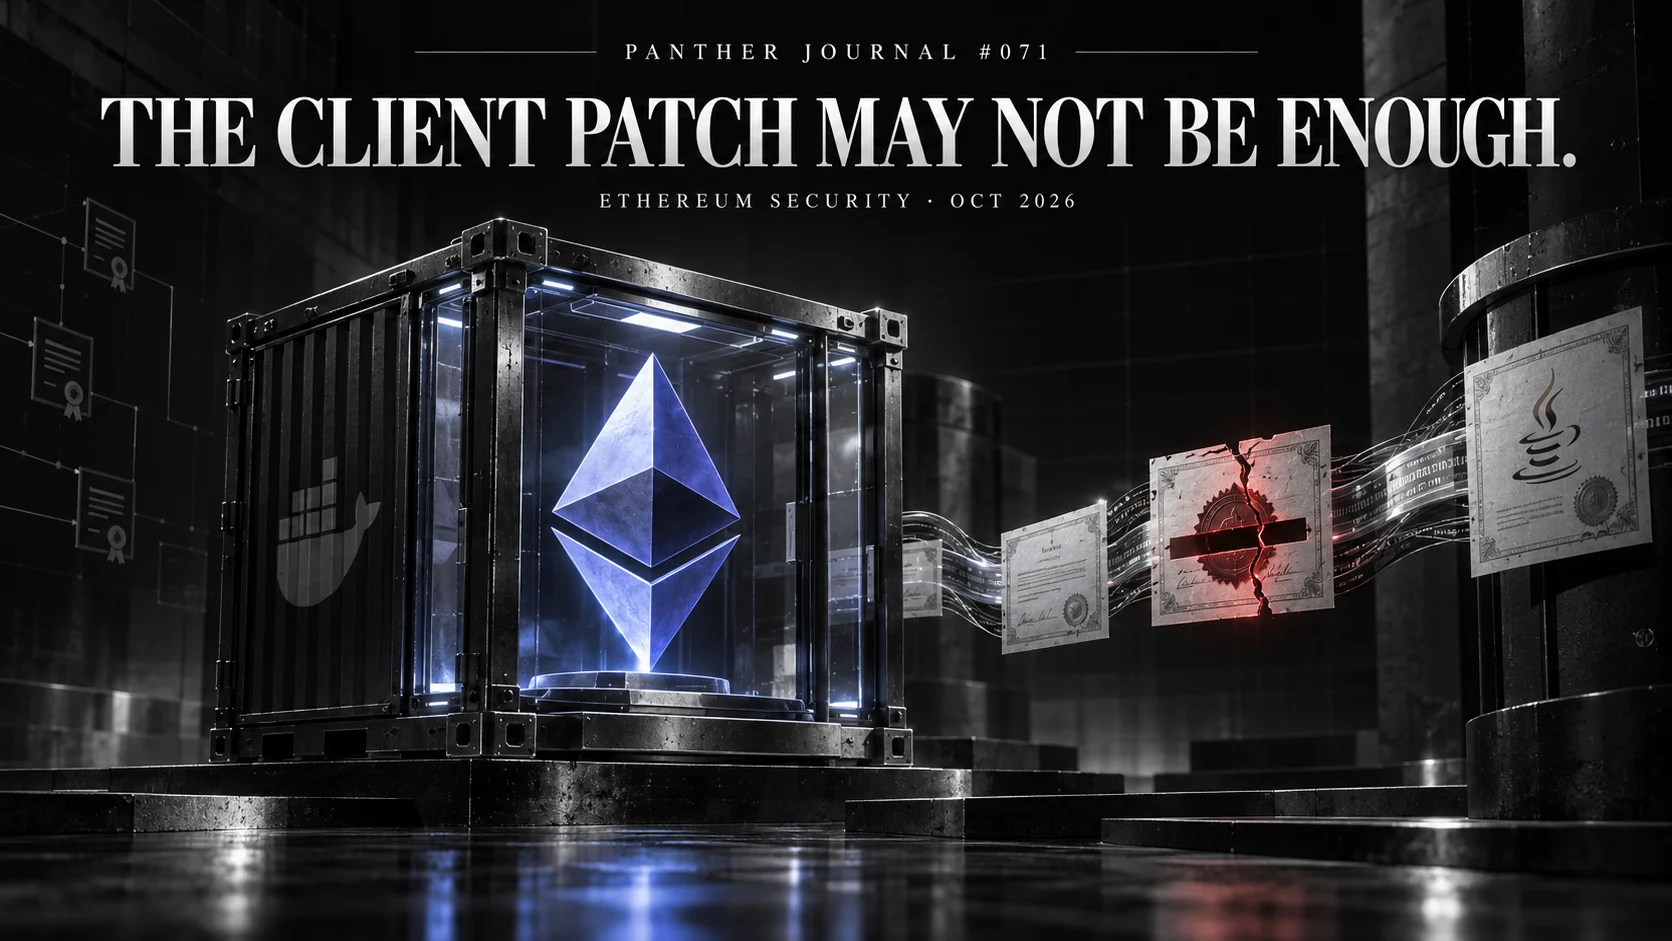
On October 17, researchers disclosed that private keys for eight intermediate certificate authorities operated by eMudhra could be recovered from their public certificates. That failure meant an attacker could create certificates that vulnerable software might accept as authentic.
The affected intermediates were revoked on October 18. Browsers and several operating systems blocked them. Java is the important exception for Ethereum operators: it does not check certificate revocation by default, so an old Java trust store could continue accepting a chain that other software had already rejected.
This is a certificate-trust failure, not a break of Ethereum’s cryptography or a theft of validator keys.
Which Ethereum operators were exposed?
The Teku security advisory says a default Teku mainnet node is not affected and needs no action. The risk appears when Teku connects over HTTPS to another host—for example, a remote beacon node, external signer, proposer configuration, builder relay, execution client or checkpoint source.
An attacker would also need a position on the network path. That could mean compromised infrastructure, hostile shared hosting, a malicious router or another route capable of intercepting the connection.
The worst outcomes depend on the endpoint. Teku says an impersonated remote beacon node could provide a block payload that directs fees to the attacker. A fake external signer could expose credentials, redirect builder registrations or request dangerous signatures if the signer lacks its own protections.
Teku reports no known exploitation. That distinction matters: the advisory describes a credible path to loss, not evidence that validator rewards were actually stolen.
Docker is patched. Archive installs have another layer.
Teku 26.10.3, released October 27, removes the affected roots from its Docker images. Besu 26.10.2, released October 26, does the same for Besu containers.
That is the clean route for Docker users: pull the fixed client image, redeploy it and verify the running version rather than assuming a downloaded image is active.
Archive and binary installations work differently. They use the Java runtime installed on the host. Updating Teku or Besu alone does not necessarily update that runtime or its certificate store. Besu’s release notes explicitly direct archive users to inspect and remediate their JDK separately.
Java 26 adds another trap. Teku says the short-term release is end of life and will not receive a fixed build, so affected operators should move to a supported Java 25 build rather than waiting for a Java 26 patch.
What should operators check now?
Start with the installation path, then the network path.
- Teku Docker: confirm the running image is 26.10.3 or newer.
- Besu Docker: confirm the running image is 26.10.2 or newer.
- Archive or binary install: check the JDK vendor’s eMudhra guidance and update the Java trust store independently.
- Java 26: migrate to a supported Java release; do not assume a fix is coming.
- Remote HTTPS services: inventory external signers, beacon nodes, relays, execution clients, checkpoint sources and proposer configuration URLs.
- External signers: prefer certificate pinning and mutual TLS where supported, and keep credentials out of URLs.
- Private infrastructure: keep sensitive client-to-client connections on localhost or a private network when possible.
Restarting without changing the image or Java runtime does not remove a trusted root. Version labels should be verified against the process that is actually running.
This operational lesson echoes Panther’s earlier Ethereum configuration warning: protocol safety can depend on mundane deployment details long before anything appears onchain.
The Panther takeaway
A patched client name is not proof of a patched trust store.
Docker users have fixed Teku and Besu images available. Binary users still own the Java layer beneath the client. Default Teku mainnet nodes were not exposed, and no exploitation has been reported—but operators using remote HTTPS endpoints should verify the full stack now.
Sources and verification
- Teku security notice: eMudhra CA compromise, updated October 28, 2026. Primary scope, affected configurations, consequences and remediation.
- Teku 26.10.3 release, October 27, 2026. Primary Docker-image fix.
- Besu 26.10.2 release, October 26, 2026. Primary Docker fix and archive-install warning.
- CoinDesk, October 29, 2026. Independent reporting on the validator impact and release status.
- CryptoSlate, October 28, 2026. Independent confirmation of the Docker-versus-binary distinction.
Responses
No responses yet. Start the conversation.
Panther Journal — The intelligence brief
Stay ahead of the story.
Free. New investigations delivered when published. Unsubscribe anytime.