Key points
- Initia says a MoveVM script-cache bug let an attacker spoof unbacked balances without minting native $INIT.
- About $2.7 million crossed through LayerZero, Noble and CCTP before Initia halted its L1 and rollups.
- The exploit-linked Ethereum wallet held 1,135.524692576255145542 ETH with no outgoing transactions when Panther checked October 25.
- A restart should be judged by the patch, audit, asset reconciliation and confirmed reopening of affected routes.
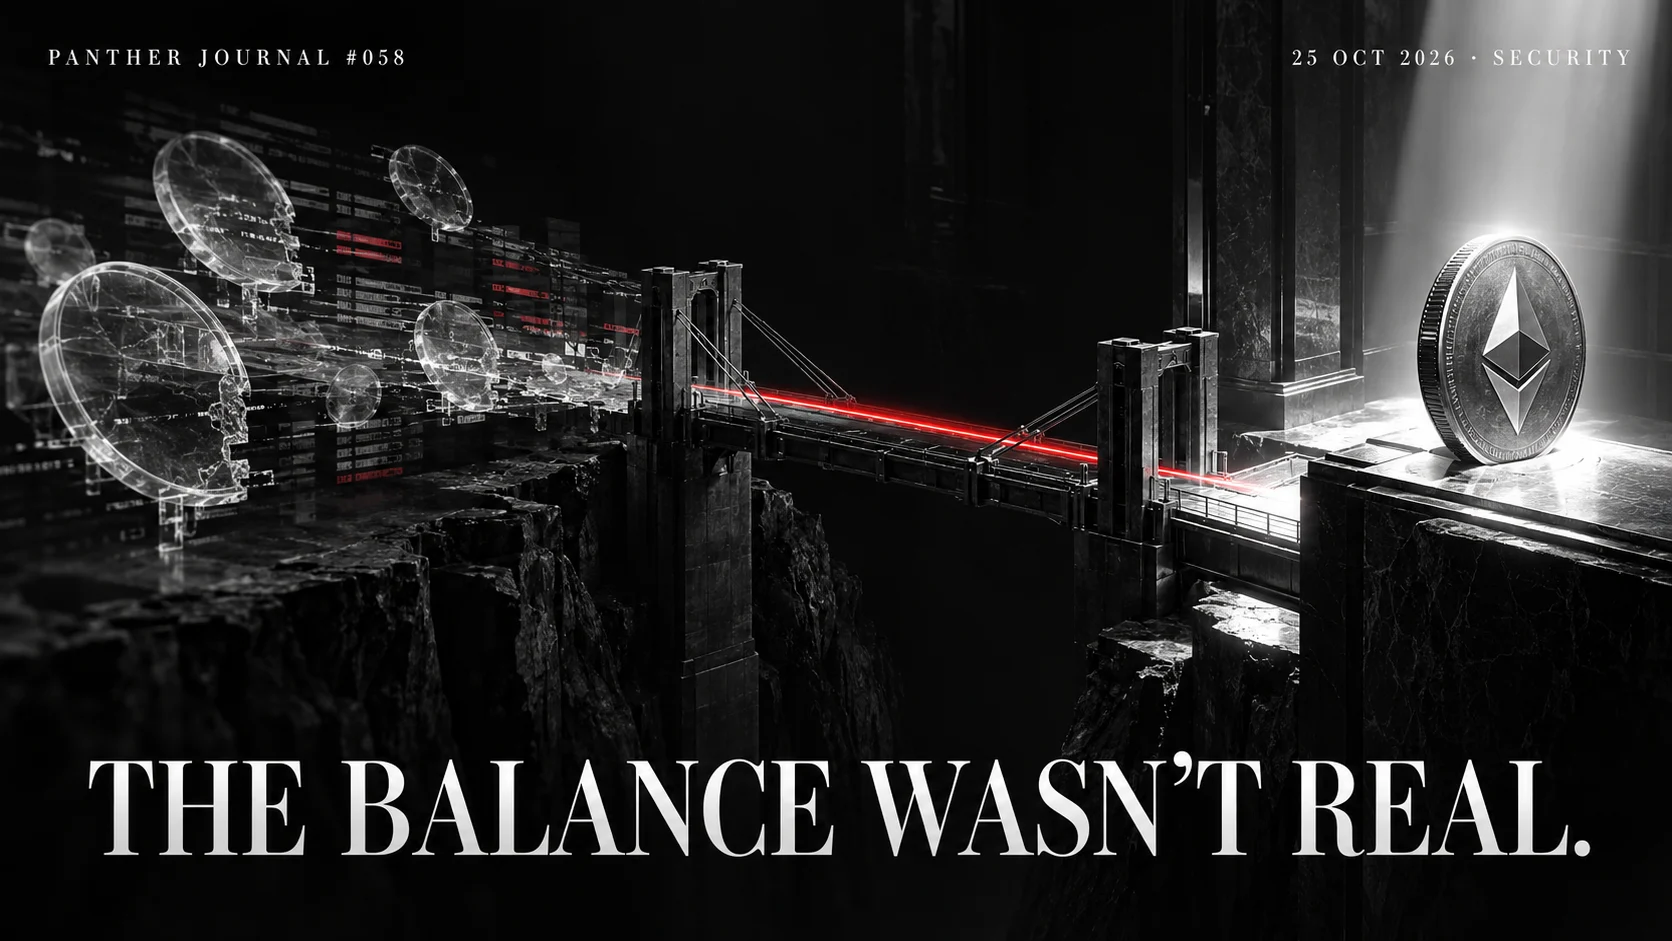
The Initia MoveVM exploit began with a balance that looked real enough to spend. The ledger looked rich. The bridge messages cleared. On Ethereum, the output was brutally real: 1,135.52 ETH sitting in a fresh wallet.
The money on the other side of the bridge had begun as something else entirely—state that Initia says an attacker fabricated inside its MoveVM. The incident is a clean lesson in cross-chain risk: a bridge can faithfully carry a lie when the chain it trusts has already been deceived.
What happened on Initia?
At 14:59 UTC on October 23, 2026, an attacker exploited a bug in Initia MoveVM’s script caching, according to the project. Initia says malicious code bypassed security checks and spoofed MoveVM state, crediting the attacker with unbacked WETH, iUSD and USDC balances.
That wording matters. Initia says the corresponding token supplies did not change and no native $INIT was minted. The attacker altered what the virtual machine believed an account owned, rather than creating additional INIT.
At 15:41:30 UTC, Initia halted its Layer 1 and rollups. Before the halt, the project says roughly $2.7 million had crossed out: 105 WETH and about 1.4 million AUSD0 through LayerZero, plus about 1.08 million USDC through Noble and CCTP. Those assets were swapped into 1,135.52 ETH.
How did the Initia MoveVM exploit create a fake balance?
A blockchain application does not inspect economic reality. It evaluates state and rules. If a bug lets an attacker make the execution layer accept a false balance, every downstream system that trusts that state can receive a technically valid message built on a false premise.
That is the dangerous handoff here. The external bridges did not need to believe a forged screenshot or an off-chain claim. They processed messages originating from the compromised Initia-side state. Real liquidity was then released on Ethereum.
This does not establish that LayerZero, Noble or CCTP were themselves exploited. Initia has identified its MoveVM cache as the vulnerable component. A full postmortem is still pending, so the exact control failure, patch and responsibility across integrations remain open questions.
What does the Ethereum trail show?
Initia linked the proceeds to 0x358e…CAC8 on Ethereum. When Panther checked on October 25, Etherscan displayed 1,135.524692576255145542 ETH and no outgoing transactions from that address. The main inbound transfer—1,135.52 ETH—arrived from 0xDD92…edFA.
The address also received three tiny inbound transfers. Those dust payments do not prove a relationship with their senders; anyone can send assets to a public address. The meaningful evidence is the large transfer identified by Initia and the wallet’s lack of outgoing transactions at the time checked.
An independent 0xCERT advisory records the exploit-linked wallet, the 1.4 million AUSD release transaction, the 105 ETH release transaction and the Initia-side transaction hash. The Block separately reported the halt and the early $2.6 million estimate before Initia published its more detailed accounting.
What should users verify before a restart?
A restart announcement alone is not the finish line. Users should look for four things: a published patch, an independent audit of that patch, a reconciliation of affected assets and explicit confirmation that deposits, withdrawals and bridge routes have reopened.
Until then, avoid links claiming to offer refunds, migrations or compensation. Initia has told users to rely on its official channels. When services resume, verify the network, token contract, bridge route and destination before moving funds. A small test transaction can reduce operational mistakes, but it cannot prove the underlying patch is safe.
If you need to inspect the public trail yourself, Panther’s guide to tracing a crypto wallet explains how to separate transactions from labels and assumptions.
Panther Takeaway
This exploit did not need to inflate $INIT. It turned false execution state into real external liquidity. The number to watch is not the token price; it is whether Initia can prove the patched chain, bridges and accounting agree on what is real.
Responses
No responses yet. Start the conversation.
Panther Journal — The intelligence brief
Stay ahead of the story.
Free. New investigations delivered when published. Unsubscribe anytime.