Key points
- Optimizely says it fixed a vulnerability used to inject malicious JavaScript into customer projects.
- Researchers report 188 poisoned snippets linked to 178 organizations; those are not confirmed visitor or loss counts.
- Review affected-page payments and the full recipient address; the wider investigation remains open.
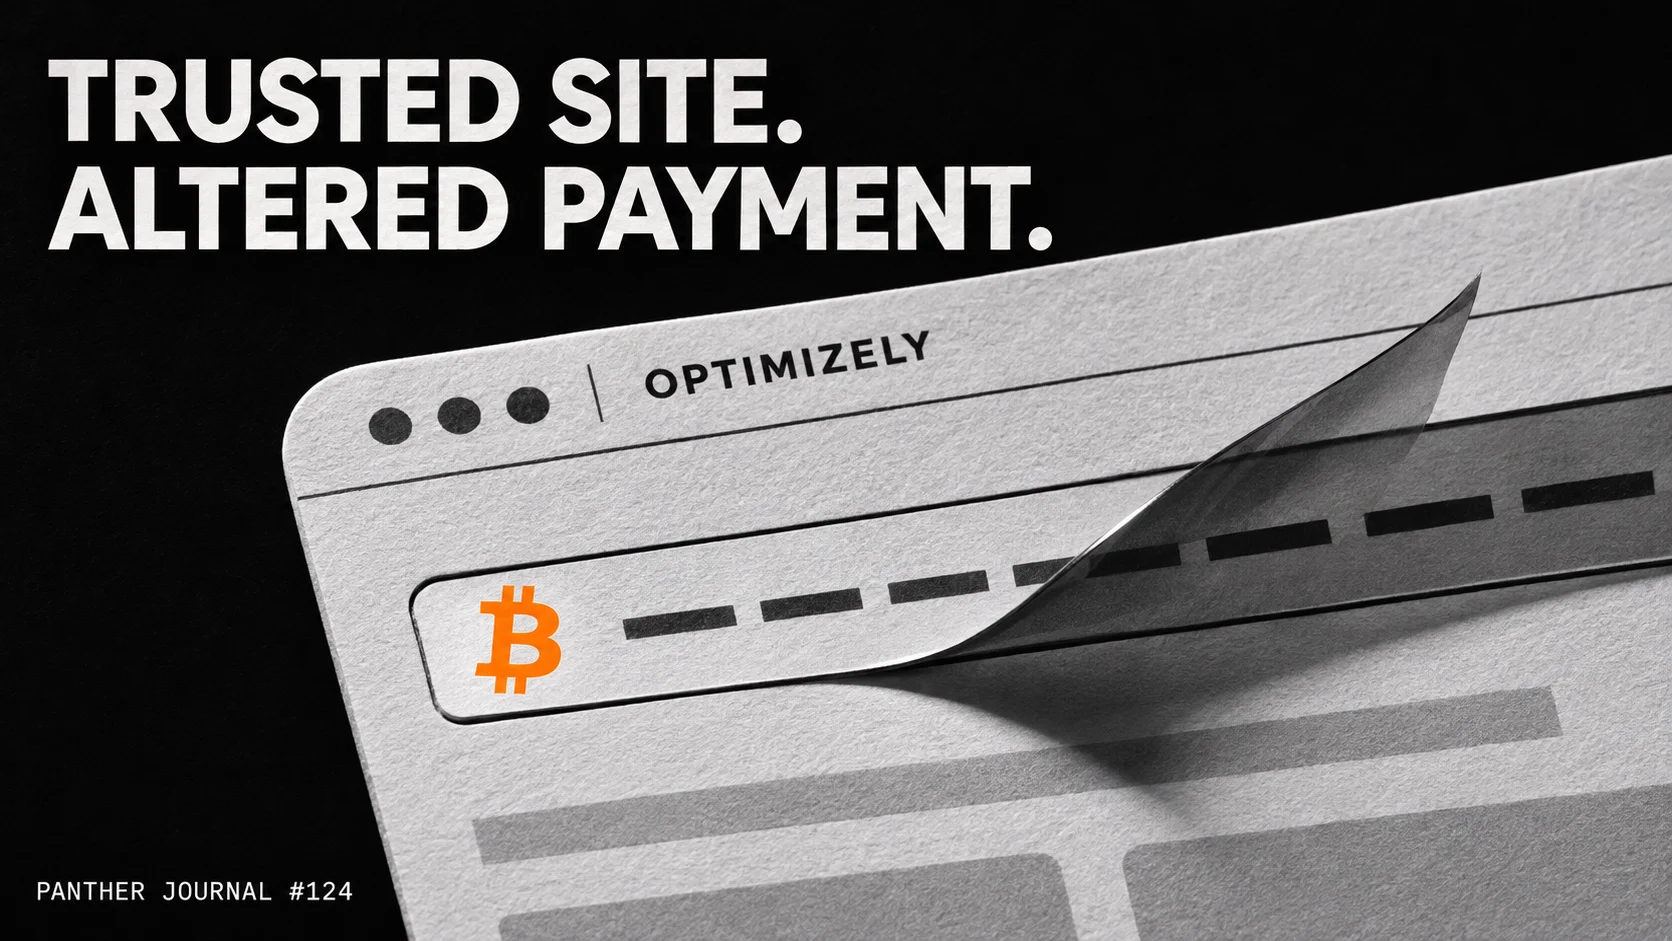
A familiar website could display an attacker’s crypto payment address. Optimizely confirmed at 01:02 UTC on November 17, 2026 that an attacker exploited its Experimentation product to inject malicious JavaScript into customer projects. The company says it fixed the vulnerability, removed the injected code and secured affected accounts. Its public incident remains marked Monitoring at this article’s check.
The new information matters beyond website operators. Readers who made crypto payments through affected pages on November 16 can check the actual transaction destination now, rather than relying on how familiar the page looked.
How the Optimizely attack crossed a trust boundary
In his November 16 investigation, Report URI researcher Scott Helme describes malicious code added to customer Project JavaScript. Legitimate Optimizely snippets then delivered it to visitors through a hostname those websites already trusted.
Helme’s review found 188 poisoned snippets associated with 178 organizations, including Zoom, the BBC, Salesforce and Ledger. Those are script and organization counts, not 178 proven backend breaches or a count of infected people. He reported only one of the previously infected snippets still contained the code at 21:52 UTC on November 16; that observation is a historical snapshot, not a guarantee that every affected page is safe today.
BleepingComputer independently examined modified files and archived website scans. It confirmed loaders and malicious capabilities, including replacement of crypto addresses, card-data collection and delivery of iOS exploit code. Its report identifies Bitcoin ($BTC) among the targeted payment-address formats. Optimizely told the outlet that the entry point was its Experimentation account signup flow.
A wider investigation, with important limits
A November 17 Hudson Rock update, checked against public material through 06:20 UTC, describes linked malicious delivery through Optimizely, Kissmetrics, StorifyMe and minute-ly. Some archived observations date to November 13.
The researchers distinguish recovered samples from historical response analysis. They have not established a common intrusion method across all four services, a campaign-wide visitor count or successful exploitation of real iPhones. Shared technical indicators alone do not identify an attacker.
Reuters reported that Salesforce disabled Optimizely scripts while investigating. Equifax stopped using the service and said it found no evidence its own systems were compromised. Reuters could not establish the extent of successful attacks. Script exposure, stolen funds and compromise of a company’s servers remain separate findings.
Check the recipient, not just the website
If you used an affected page on November 16:
- Compare any crypto transfer’s full destination with the intended recipient through an independent, established channel. Keep the transaction hash if something differs.
- Review payment-card activity and contact the issuer about suspicious transactions. Install current iOS or iPadOS security updates through device settings.
- Watch for unusual account activity, especially if you were signed into sensitive services at the time. Follow the affected service’s verified security guidance.
For future transfers, check the complete destination again on the signing screen. Panther’s recipient-verification guide explains that checkpoint. The mechanism here is malicious webpage code; a trusted display still needs an independently verified address to compare against.
Panther Takeaway
A familiar domain cannot certify every script running inside a page. Optimizely’s reported fix addresses the injection route; it does not establish which earlier visitors lost data or funds. Verify the recipient from outside the affected page, preserve suspicious transaction evidence and keep exposure counts separate from confirmed harm.
Responses
No responses yet. Start the conversation.
Panther Journal — The intelligence brief
Stay ahead of the story.
Free. New investigations delivered when published. Unsubscribe anytime.